Black Kite Introduces Quantum Readiness Controls to Assess Third-Party Cryptographic Risk
Black Kite has launched Quantum Readiness, a new feature in its Cyber Rating engine that assesses third-party vendors' preparedness for post-quantum…
Third-party cyber risk management platform provider Black Kite has announced the launch of Quantum Readiness, a new control set integrated into the SSL/TLS Strength category of its Black Kite Cyber Rating engine to evaluate post-quantum cryptographic (PQC) agility across third-party vendor supply chains.
The feature provides organizations with external visibility into vendor cryptographic postures, identifying which third-party software, cloud, and IT providers have implemented quantum-resistant encryption methods—such as hybrid post-quantum key exchange and PQC certificate signature readiness—or remain reliant on legacy algorithms facing regulatory phase-outs. The rollout addresses mounting regulatory compliance deadlines, including U.S. Office of Management and Budget (OMB) M-26-15 guidelines mandating post-quantum key establishment by 2030 and digital signatures by 2031, Executive Order 14412 contractor migration targets, and European Union NIS2 supply chain cryptographic mandates.
[ Black Kite Quantum Readiness Framework & Regulatory Benchmarks ] | ||
Assessment Pillar | External Observable Signal | Target Regulatory Compliance Driver |
• Key Exchange Agility | • Detection of active hybrid PQC key exchange mechanisms | • OMB M-26-15 U.S. Federal key establishment migration deadline (2030). |
• Certificate Readiness | • Inspection of PQC-ready digital signature certificates | • Executive Order 14412 Federal Acquisition Rule contractor standard (2030). |
• Asset Vulnerability Mapping | • Identification of unmigrated legacy assets (RSA/ECDSA/ECDH) | • NIST deprecation schedule (post-2030) and complete disallowance (2035). |
• Supply Chain Risk Integration | • Integration into SSL/TLS Cyber Rating ecosystem scoring | • EU NIS2 Directive supply chain risk management obligations (2026/2030). |
By automating continuous observation of external cryptographic signals across vendor supply chains, Black Kite aims to help enterprises and government agencies mitigate "harvest now, decrypt later" vulnerabilities prior to mandatory national PQC migration deadlines.
Review the press release via Black Kite Pressroom here.
October 21, 2026
Related Intelligence

Test of USydney article with HTML.
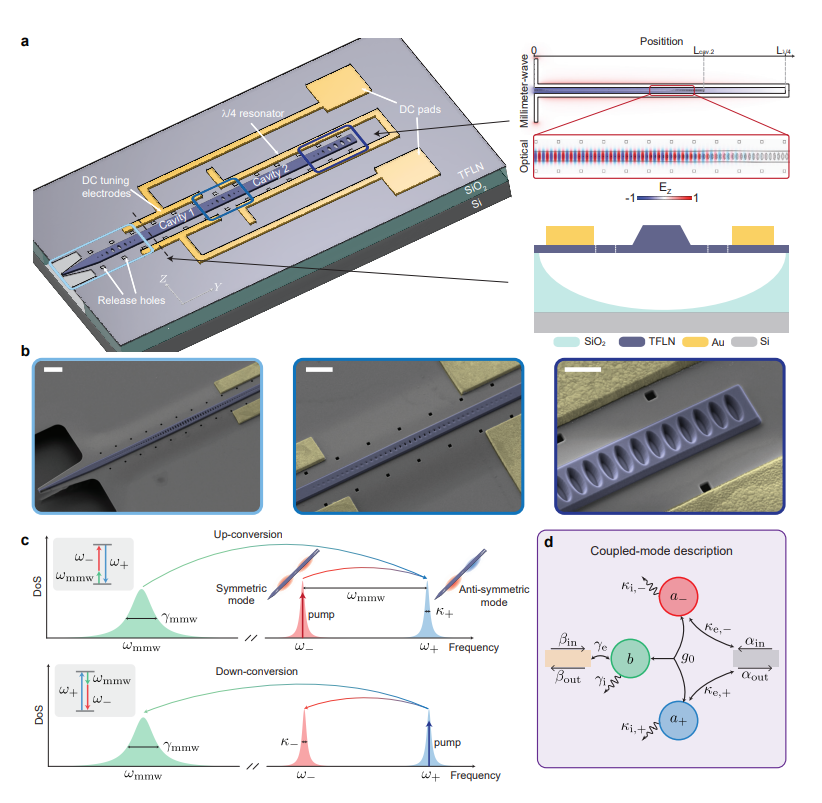
EPFL Demonstrates Millimeter-Wave-to-Optical Transducer with 67% Internal Efficiency
November 10, 2026
Why Quantum Hardware Needs Its Own Threat Model
November 9, 2026
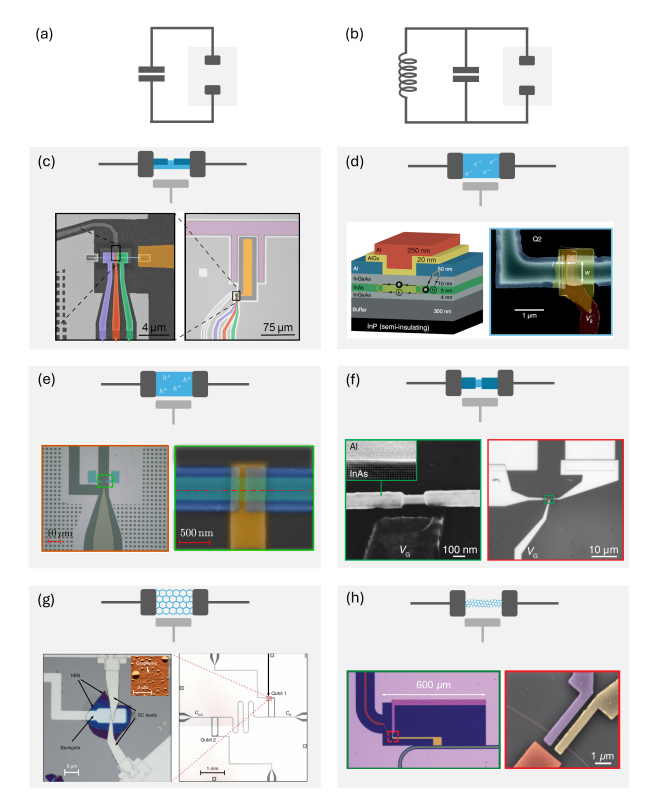
Physics Reports Analysis Evaluates Emergence of Hybrid Semiconductor–Superconducting Qubit Architectures
November 9, 2026
DLR Develops Scalable Unitary Data Encoding Beating Exponential State-Preparation Depth
November 9, 2026
IonQ and Classiq Outline Architectural Trade-Offs in Fault-Tolerant Resource Estimation
November 9, 2026